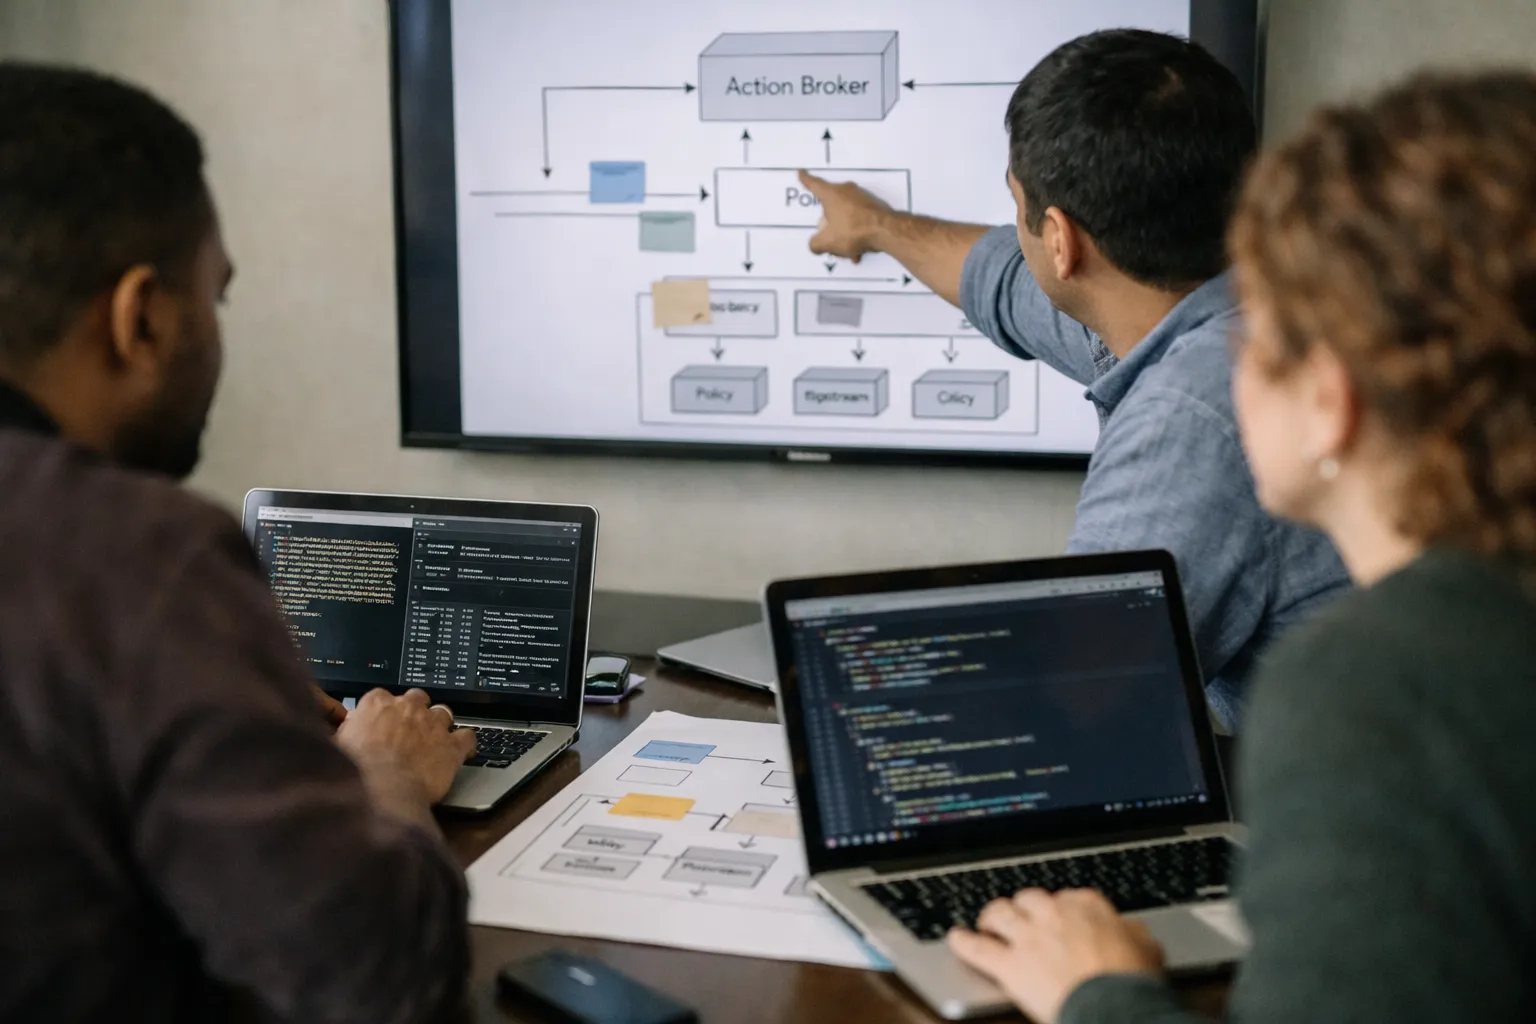
Enterprises are running AI assistants and autonomous agents deeper into business processes—approving invoices, managing payroll, reconciling accounts, and invoking third‑party APIs. By September 2026 the operational reality has shifted: organizations no longer ask whether models will "hallucinate" answers but how those models will be allowed to take actions. This updated guide gives technical leaders a compact, practical playbook for enforcing least‑privilege on AI action execution: concrete design patterns, implementation steps, observable controls, and operational KPIs you can apply now.
Who this is for and why it matters
This guide is for platform engineers, security architects, product managers responsible for AI automation, and compliance teams. If your organization uses assistants or autonomous agents to perform actions in ERP, HR, finance, or customer systems, you need a least‑privilege model that: limits what agents can do, shortens the time window for actions, produces auditable provenance, and supports rapid remediation.
Prerequisites / context
Before you begin, ensure you have:
- Inventory of systems and APIs the assistant will touch (ERP, CRM, payment rails).
- Standard identity primitives in place (workload identities, mTLS, or cloud managed identities).
- Centralized logging and a SIEM/tracing pipeline for structured telemetry.
- A policy engine or governance point you can call at decision time (Open Policy Agent or cloud IAM policy checks).
What’s new in Sept 2026 — short summary
- Capability‑based authorization has moved from experimental to mainstream architectures: more organizations map operations (e.g., invoices:approve) to tokens rather than reusing service keys.
- Short‑lived tokens and token‑exchange flows (RFC 8693) are widely adopted as production patterns; cloud providers' STS and workload‑identity features are the default integration points.
- Tooling for model and action provenance (model cards, signed action attestations) is maturing; teams are integrating artifact signing and Sigstore‑style attestations into action pipelines.
- Regulatory scrutiny and audit focus on “actionable AI” has increased—auditors expect provenance, consent trails, and revocation paths for automated actions.
Core design principles (refreshed)
- Capability-first authorization: Define capabilities per discrete business operation, not coarse roles.
- Ephemeral, contextual credentials: Issue single‑purpose tokens tied to user/session provenance and expiration measured in minutes for high‑risk operations.
- Policy‑as‑code decisioning: Centralize rules (OPA/Rego or cloud policy) with CI/test coverage and audit trails.
- Privileged proxy (Action Broker): A hardened mediator that authenticates the assistant, verifies intent, runs policy, performs token exchange, and calls downstream services.
- Provenance & attestation: Record model version, prompt transcript (redacted for PII), confidence metrics, and signed attestations of decisions.
- Human gating for high risk: Multi‑party approval, canary executions, and staged rollouts for irreversible or high‑impact actions.
Reference architecture (high level)
The architecture still centers on a small set of components. Implementation details below reflect patterns seen in production in 2026.
- AI frontend / assistant: Chat UI or agent framework that emits an action intent with provenance metadata (user, session, model id).
- Action Broker / Privileged Proxy: Authenticates assistants, maps intents to capabilities, enforces policy, and orchestrates token exchange.
- Token Broker / STS: Exchanges broker identity for scoped, short‑lived credentials using cloud STS or an internal RFC 8693 token exchange service.
- Downstream services: ERP, HR, payments—accept scoped credentials or only accept calls from the broker’s mTLS identity.
- Policy Engine & Audit Store: OPA or cloud policy evaluation, structured audit logs, and immutable storage (WORM or SIEM retention) for forensic trails.
Typical flow (concise)
- User asks assistant to take an action (e.g., "Approve vendor invoice #4321").
- Assistant emits intent payload: action id, user id, session id, model id, transcript, confidence.
- Action Broker authenticates the assistant (workload identity / mTLS), looks up the capability, and calls the policy engine.
- If allowed, broker requests a narrowly scoped, short‑lived token from the Token Broker / STS and calls the downstream API.
- Broker records the decision, token metadata (IDs, expiry), and downstream response in immutable audit storage.
Step‑by‑step implementation guide
1. Inventory and classify actions
Do this with domain owners and product teams. For each operation record:
- Action name and description (e.g., invoices:approve_payment).
- Business impact: Low / Medium / High.
- Data classification: Public / Internal / Confidential / Regulated.
- Required downstream permissions or roles.
- Approval model: Automated / Human approval / Multi‑party.
Concrete example: invoices:create_draft = low impact, internal data; invoices:execute_payment = high impact, confidential, requires two approvers and 2FA.
2. Define capability tokens and scopes
Create a capability taxonomy and map it to scope strings (e.g., invoices:read, invoices:approve:under_10k). Design tokens to be:
- Single‑purpose where feasible (one capability per token).
- Short‑lived: minutes for high‑risk, up to hours for low‑risk automation.
- Bound to provenance: include user id, session id, model id, and broker request id in token claims.
3. Build the Action Broker (privileged proxy)
Principles:
- Treat the broker as a security boundary: minimal attack surface, hardened platform, strict patch cadence.
- Enforce strict authentication for assistant frontends (workload identity + mTLS or OAuth2 with signed JWTs).
- Integrate OPA or cloud policy API synchronously; record policy decision IDs with each action.
- Support dry‑run and canary modes for new capabilities to observe effects before live rollout.
Operational tip: run the broker on an isolated subnet with egress rules and dedicated observability pipelines; require blue/green deployments and security reviews for broker changes.
4. Use token exchange and short‑lived credentials
Implement an exchange flow where the broker's identity is traded for a token scoped to a single capability. Options:
- Cloud STS (AWS, GCP, Azure) to mint ephemeral role credentials tied to claims.
- Internal token broker implementing RFC 8693 for enterprise‑specific claims and attestation.
- Hardware‑backed key signing for non‑repudiation where required.
Ensure downstream services validate both the token scopes and provenance claims (e.g., require the request include the action intent ID and model id).
5. Enforce policy with OPA and policy‑as‑code
Centralize authorization checks. Best practices:
- Keep policies small and test them with unit tests and policy CI pipelines.
- Version policies and keep the historical decision outcomes for audits.
- Simulate policy changes against traffic snapshots to estimate false positives before rollout.
6. Human approvals and staged execution
For high‑impact actions implement these controls:
- Approval UI that shows full provenance: transcript, model id, confidence, and prior related actions.
- Multi‑signatory workflows with independent approver sets and timeouts.
- Staged execution: dry run → canary account → full execution after observed metrics meet safety SLOs.
7. Observability, auditing and incident response
Audit events should include:
- Action intent ID, user ID, session ID, model version, and hashed transcript (redact PII).
- Policy decision ID and rule evaluation results.
- Issued token ID (not the raw token), capability list and expiry.
- Downstream request/response hashes, HTTP status codes, and timestamps.
Operationalize runbooks: how to revoke tokens quickly, how to roll back downstream state, and how to quarantine an assistant or model. Aim for a mean time to revoke credential of minutes for high‑risk capabilities.
Testing and validation (2026 practices)
Expand testing to include adversarial prompt testing and model‑level tests:
- Unit tests for policy rules and broker logic.
- Integration tests that exercise token exchange and downstream calls against sandbox systems.
- Adversarial tests: prompts crafted to escalate privileges, chain actions, or bypass prompts (run by red teams or automated fuzzers).
- Chaos tests simulating broker compromise: validate revocation and containment paths.
Operational metrics and KPIs
Track both security and performance metrics:
- Number of AI‑initiated high‑risk actions executed per week (and approvals required).
- Mean time to revoke credential (target: 10 minutes for high‑risk tokens).
- Policy decision latency (SLO: 50–150 ms for interactive assistants).
- Percentage of actions executed using scoped tokens vs. wildcard/emergency tokens (goal: > 98% scoped).
- False positive/negative rates in policy enforcement and human approval queues.
Common pitfalls and how to avoid them
- Monolithic privileges: Avoid granting assistants broad service tokens; start with a small capability surface.
- Poor provenance capture: Capture user, session, model id, and hashed transcript — don’t rely on truncated logs for forensic review.
- Neglecting revocation: Ensure you can revoke tokens and disable brokers fast; test the revoke path regularly.
- Performance blindspots: Validate that policy checks and token exchanges meet your assistant latency requirements; pre‑cache safe decisions where appropriate.
Pro tips (advanced)
- Sign action intents with hardware‑backed keys and store attestations in an immutable store (for non‑repudiation and audit).
- Leverage model governance artifacts (model cards, versioned deployments) and include model id in every audit event to link decisions to model behavior.
- Use risk‑based token lifetimes: minutes for high‑risk actions, longer for low‑risk readonly tasks.
- Instrument feedback loops: feed policy decisions and incidents back into model‑testing suites to reduce repeat errors.
Updated tooling and ecosystem notes (Sept 2026)
Recommended, widely used components in 2026:
- Open Policy Agent (OPA) and Rego for policy evaluation and policy‑as‑code.
- Workload identity patterns (SPIFFE/SPIRE), cloud STS and workload identities (AWS, GCP, Azure) for short‑lived credentials.
- RFC 8693 token exchange pattern implemented either via cloud STS or internal token broker.
- Sigstore or similar attestation solutions for signing action artifacts and model artifacts where non‑repudiation is required.
- Standard SIEM/tracing stacks (Elastic, Splunk, Datadog) with structured audit logs ingestion for forensic queries.
8‑week rollout checklist (practical timeline)
- Week 1–2: Inventory actions, classify risk, and define capability taxonomy with domain owners.
- Week 3–4: Prototype Action Broker and OPA policies; integrate one low‑risk downstream (e.g., draft invoice creation).
- Week 5: Add token exchange and short‑lived credentials; enable structured logging and telemetry.
- Week 6: Run adversarial tests and implement human‑approval UI for medium‑risk actions.
- Week 7: Expand to critical systems, add revocation playbooks and incident response runbooks.
- Week 8: Compliance review, policy versioning CI, and phased production rollout with canary groups.
Common mistakes — concise
- Granting assistant broad admin tokens for speed.
- Not binding tokens to provenance (user/model/session).
- Forgetting to test revocation behavior under load.
- Underestimating the need to tie actions back to model versions for root cause analysis.
FAQ
How do I decide which actions require human approval?
Classify by business impact and reversibility. Require human approval for actions that are high impact, irreversible (payments, personnel changes), or that touch regulated data. Use a risk matrix: high impact + high sensitivity = multi‑party approval; medium impact + internal data = single approver or automated with enhanced logging.
Can downstream systems be changed to accept scoped tokens directly?
Yes—where feasible update downstream APIs to validate scoped tokens and provenance claims. If modifying legacy systems is impractical, require that only the broker's mTLS identity can call the legacy service and enforce capability checks in the broker layer.
What should be in the audit log to satisfy auditors?
Include action intent ID, user and session ids, model id and version, hashed or redacted prompt, policy decision id, token id (not raw token), token expiry, downstream request/response hashes, and timestamps. Retain logs according to regulatory retention requirements and store them immutably when needed for forensic purposes.
How fast should token revocation be?
Targets vary by risk: for high‑risk capabilities aim to revoke within minutes; for low‑risk read operations, hours may be acceptable. The important part is to test revocation under load and have playbooks to disable broker issuance quickly if suspicious activity is detected.
How do I handle PII in prompts and transcripts?
Redact or hash PII before storing in audit logs, and limit storage of raw prompts to secured, access‑controlled buckets. Use granular access controls to restrict who can view unredacted transcripts, and consider retaining only hashed digests for long‑term traceability.
Conclusion
By Sept 2026, least‑privilege for AI action execution is a practical engineering pattern, not just a theoretical ideal. Implementing it requires capability modeling, short‑lived scoped tokens, a hardened Action Broker, policy‑as‑code, and robust observability. Start small—protect a narrow set of high‑value actions, iterate on policy and telemetry, and expand. The controls described here will help your teams unlock AI productivity while maintaining auditable, revocable, and low‑blast‑radius actioning capabilities.